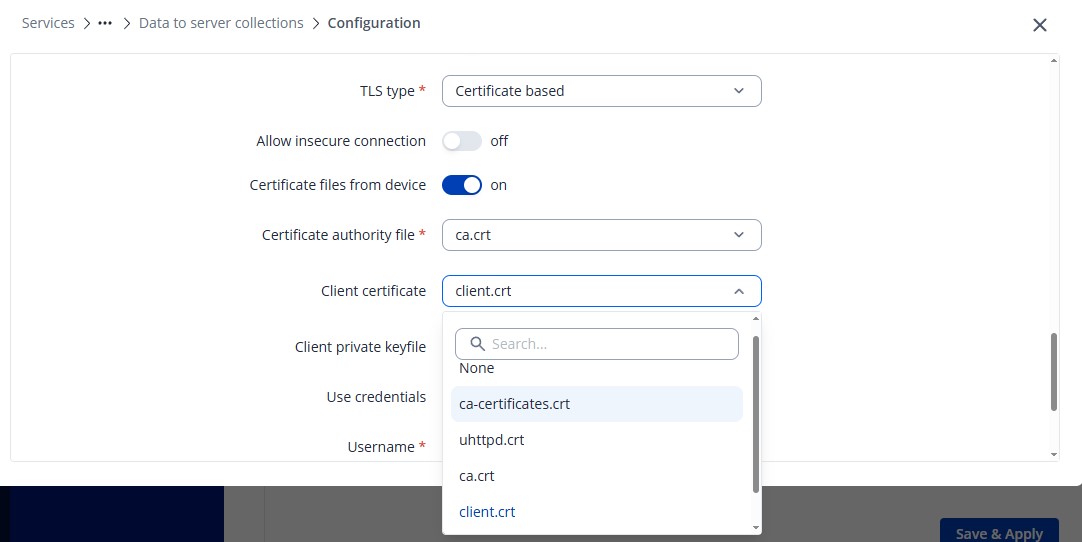
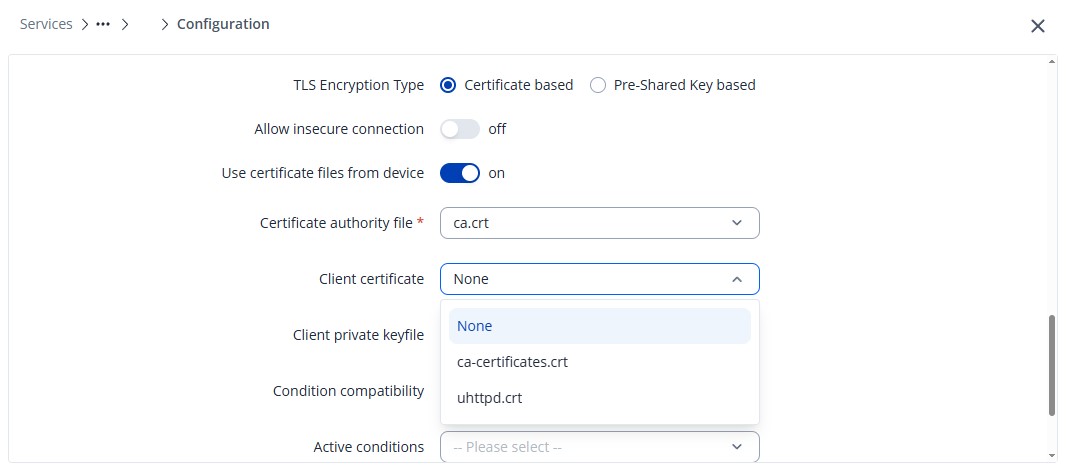
I’m using TRB246 & RUT361 devices and on firmware 7.22.3 & 7.23.1 and I have imported valid certificate authority, client certificate and client key files.
These work OK in the Data to Server module, when I select “Certificate files from device”. The files are shown in the drop-down lists and can be selected and work OK.
However, when I try and use these files in the Event Juggler, the client certificate is not shown in the drop-down list. If I load the certificates directly using the “browse” option, then everything works OK.
Why does the drop-down list in the Event Juggler not show the client certificate, while it is shown in the drop-down list in the Data to Server module?
From your description, the imported CA certificate, client certificate, and private key are successfully recognized by the Data to Server service and TLS authentication works correctly when selecting certificate files from the device. However, in Event Juggler, the client certificate does not appear in the drop-down list even though the same certificate functions correctly when uploaded manually through the Browse option.
To investigate further, could you please provide:
Screenshots of the certificate selection page in both Data to Server and Event Juggler.
The exact Event Juggler action type being used (MQTT, HTTP(S), etc.).
Confirmation whether the certificates were imported through System → Administration → Certificates.
As a temporary workaround, if manual certificate selection via the Browse option works correctly, please continue using that method while we investigate the certificate listing behavior.
The three certificates were imported through System → Administration → Certificates.
The Event Juggler action type being used is MQTT.
Attached are the screenshots of the drop-down lists for the client certificate in the Data to Server service and for the Event Juggler service. As you can see the drop-down list in the Data to Server service includes the client.crt file which works OK, whereas in the Event Juggler service the client.crt file is missing.
As there are a number of event juggler items configured, I don’t want to manually load a separate set of certificates for each action as when they need renewing they will have to be all manually loaded again. A single set loaded on the device will be easier to update quickly.
In the meantime, as a workaround, I’ll try using the MQTT Broker bridge as this allows me to load all three certificates directly from the device. I can then write the MQTT data to the external broker via the bridge at 127.0.0.1 from the Data to Server and Event Juggler services.
For troubleshooting purposes, we will require more sensitive information from your end, such as the troubleshoot file, which may contain passwords, public IP addresses, serial numbers, and such. To avoid leaking this information, we have sent you a form to fill out, which you will receive in your e-mail inbox that you have registered your account with in the forums. In the **Ticket ID** field of the form, please enter the ID of this thread, which is 19659.