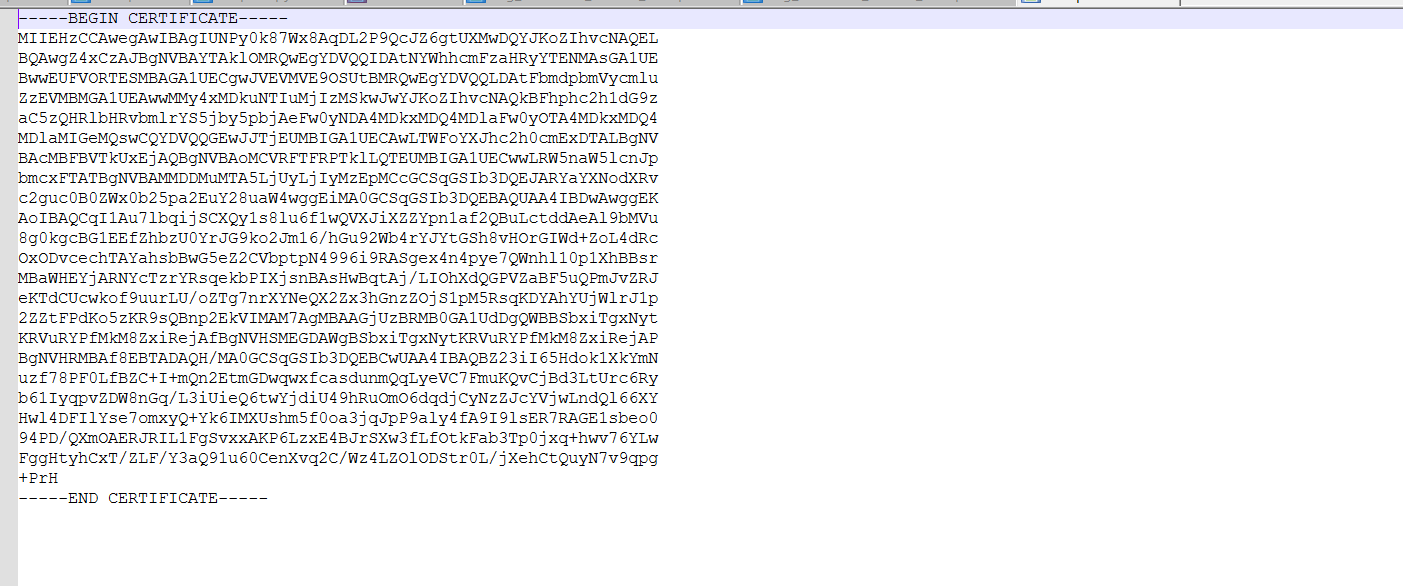
I have 3 files (root.pem, device.pem.crt, and device.pem.key), which were successfully uploaded using teltonika configurator USB. And all files are PEM formatted (contain -----BEGIN and -----END).
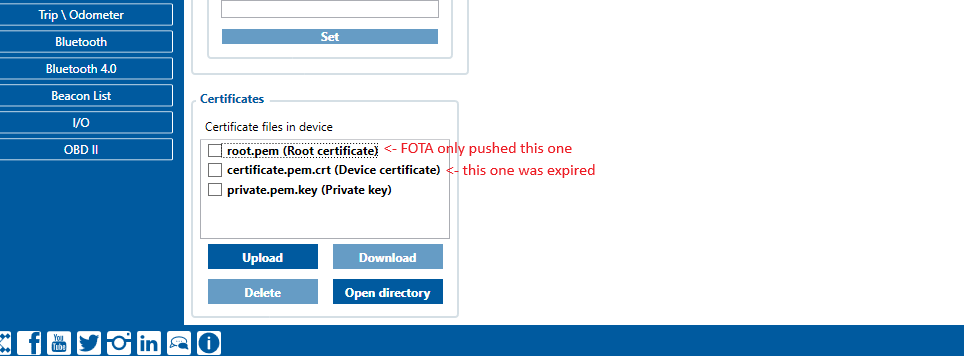
But, no matter which combination and permutation I use during uploading to FOTA, FOTA task only pushes root.pem (root certificate) to the FMC (verified by connecting teltonika configurator through USB and checking the Security->Certificate menu).
So, in essence, does FOTA web only support pushing root certificate? Does it not support the device certificate or its private key?
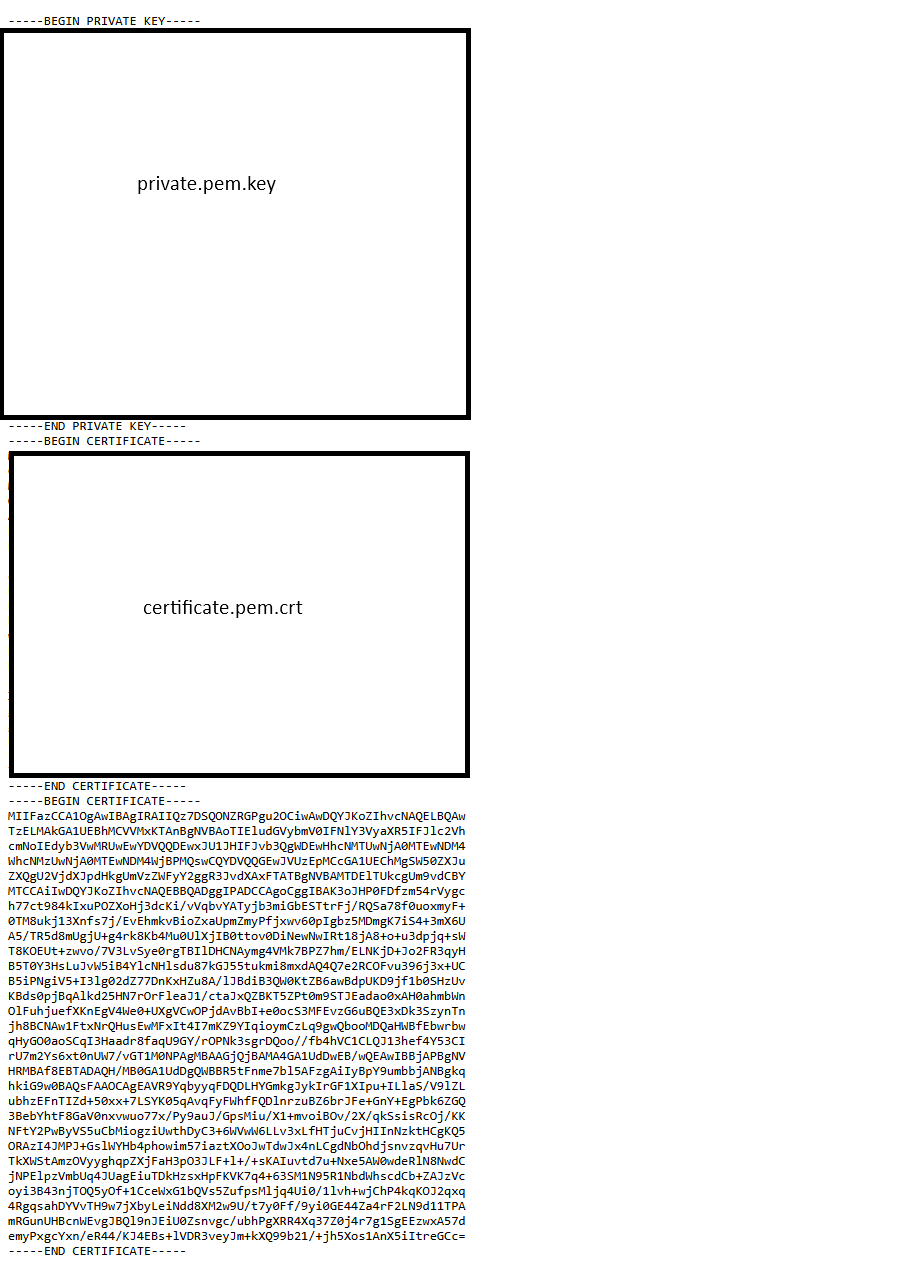
You need to push the certificate by combining the private key and device key with the root.pem certificate. Once combined, please upload the updated root.pem certificate to the device.
Based on your clue, I found the solution but only for blank or new device. To push device certificate through FOTA, I need to create just single .pem file with the specific order: private key → device cert → root cert.
Based on my testing, the following certificate.pem.crt also needs to be pushed from FOTA, or deleted entirely along with the private.pem.key file, for client cert TLS to works.
Remote removal of the certificate via SMS or via fota, is not available if the certificate was uploaded through USB or Bluetooth.
You can try the following procedure via FOTA and check whether it resolves the issue:
First, disable TLS in the configuration file and upload via fota. Alternatively, you can disable it using the following SMS command: SMS_login> <SMS_password> setparam 2020:0;
Send the cpureset command.
Prepare a single root.pem certificate containing all the required certificates combined.
Upload this certificate via FOTA and check whether the device connects and works correctly.
If the issue still persists after trying the above steps, the device may need to be checked manually.
I think proper certificate removal should be added to the future roadmap for either FOTA Web or firmware updates, as certificate expiration is inevitable.
Anyway, thank you for looking into this. We will try to recall our fleets or set the server to trust expired cert.